Scriptoria achieves ISO certification for information security and quality management
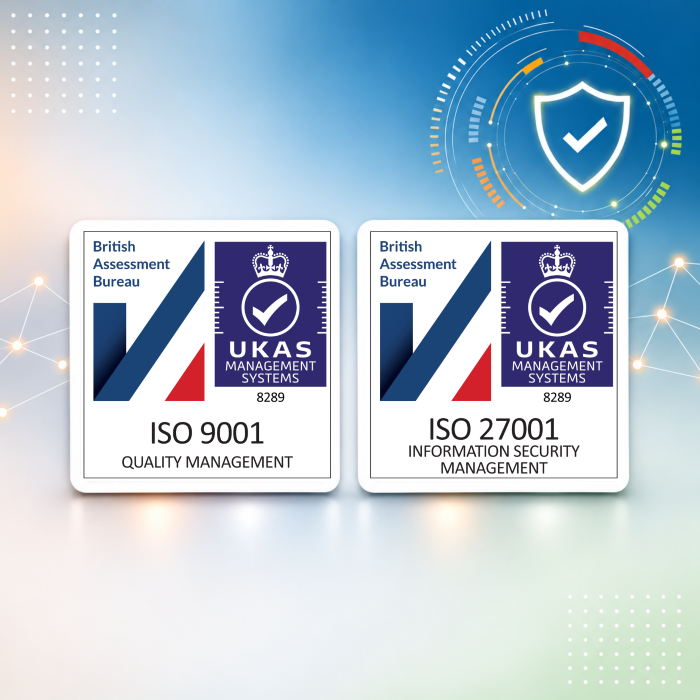
We are proud to announce that Scriptoria has achieved ISO 27001 and ISO 9001 certification, marking an important milestone in our continued investment in information security and the quality of our services.
Scriptoria’s clients depend on us to manage complex international projects, develop reliable systems and handle information responsibly. These certifications provide them with independent assurance that our information security and quality management systems meet internationally recognised standards.
Certification followed an intensive four-day independent audit by the British Assessment Bureau, which examined our policies and procedures alongside evidence of how we apply them in everyday work.
Building on our existing Cyber Essentials Plus certification (the higher level of the UK Government-backed Cyber Essentials scheme) these certifications recognise the care our teams put into their work and reinforce our commitment to keep improving. As we support clients across sustainable development, we will continue investing in the people, systems and working practices that help us deliver work they can trust.
This is critical in today’s rapidly evolving cyber landscape. The UK Government’s latest Cyber Security Breaches Survey found that 43% of businesses and 28% of charities had identified a cyber breach or attack in the previous 12 months. This figure rose to more than half among businesses in the professional, scientific and technical sector.
Dr Sandy Williams, Founding Director, said: “Cyber threats are becoming more sophisticated, especially with the rise of AI and automated attacks. ISO 27001 is just one of the ways that Scriptoria is working to stay ahead of the curve and continue protecting our clients’ information.”
The achievement reflects contributions from across all of Scriptoria. Dr Laura Knogler, Senior Knowledge Management Consultant and Head of Training, led the process and reflected: “The certification process was challenging, but the whole team’s engagement made it much easier. It was particularly encouraging that our auditor recognised their contribution.”
ISO 27001 is the internationally recognised standard for information security management, providing a framework for protecting information, managing risks and maintaining effective security controls.
Complementing this, ISO 9001 focuses on quality management systems, helping us consistently meet client requirements, maintain service quality and continually improve how we work.